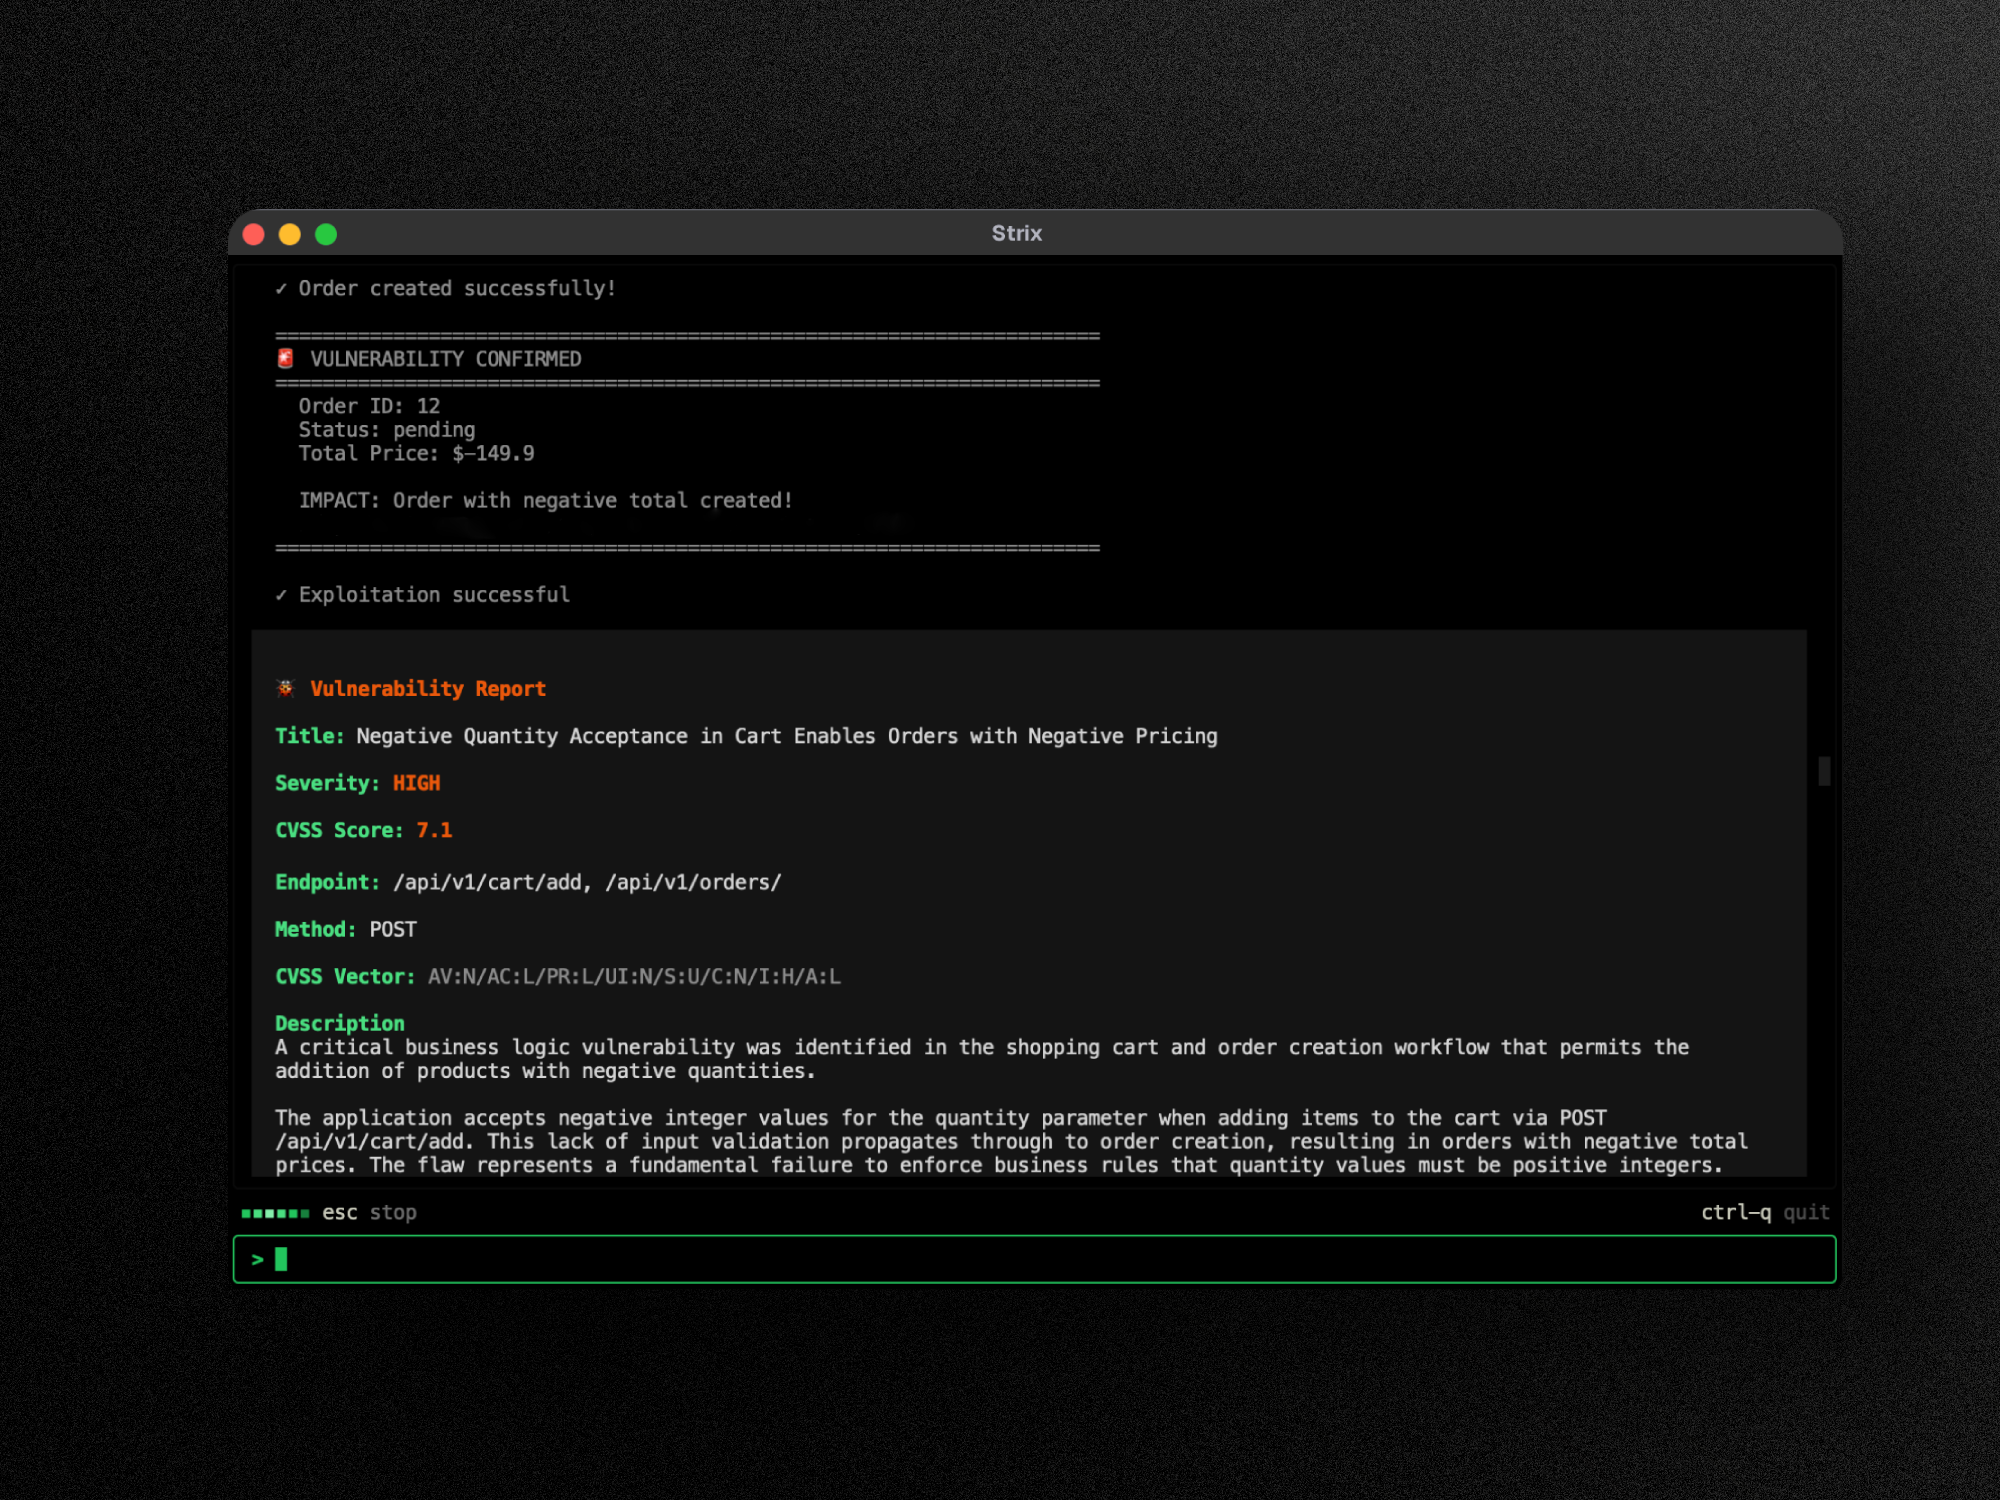
Picture published by the creator on GitHub.
Strix: Test app vulnerabilities and get repair guidance
Added · Updated

Made by Strix
View profile on GitHub (opens in a new tab)Test running apps for security flaws with this tool for developers and security teams, producing exploit evidence and repair guidance.
What it does
Strix automates penetration testing: checking an application by attempting to exploit security weaknesses. Its AI testing workers run code dynamically and try to validate findings with proofs of concept, meaning working demonstrations of a flaw. The command-line tool provides findings with repair guidance, while its reporting and repair features can generate patches and penetration-test reports.
How to use it
Open the repository's quick start, have Docker running and supply an API key from a supported language-model provider. Follow the installation and first-scan instructions to test your application. The initial run downloads the sandbox Docker image automatically. Scan results are saved locally for inspection, with findings and remediation guidance as the useful output.
Common use cases
- Test an application and receive vulnerability findings backed by exploit demonstrations.
- Connect testing to pull requests so detected vulnerabilities can block insecure changes before production.
- Use detected security findings to generate repair patches and a penetration-test report.
Can I use this?
Requirements The local version requires running Docker and your own language-model provider API key. A separate hosted Strix Cloud service offers testing and repair features without local setup. Local RAM, GPU and operating system requirements are not documented.
Caveat The source describes exploit validation but does not document a guarantee of complete vulnerability coverage. Local operation still depends on Docker and access to the selected model provider.
Worth knowing Local runs require Docker and your own model-provider key. Test coverage guarantees are not documented. Licensed under Apache License 2.0.
Why it's here
Not trending this week
Last seen on the GitHub trending list on 22 October 2026. It stays on BuildTube so you can still find it.
- 74,361 people have starred it on GitHub.
Numbers checked on 8 November 2026; not refreshed since.
Behind it
View setup guideBuildTube has not run or verified this project. Everything above is written from what the creator published.
Made this?
Quick questions
- What is Strix?
- Strix automates penetration testing: checking an application by attempting to exploit security weaknesses.
- What can I use Strix for?
- Test an application and receive vulnerability findings backed by exploit demonstrations; Connect testing to pull requests so detected vulnerabilities can block insecure changes before production; Use detected security findings to generate repair patches and a penetration-test report
- Can I run Strix on my computer?
- Strix runs on your own computer with Docker running and your own AI model provider key; a separate hosted Strix Cloud service needs no local setup. Local RAM, GPU and operating system requirements are not documented.
- What do I need to use Strix?
- For local use, Docker must be running and you need an LLM provider API key.
- What license does Strix use?
- Licensed under Apache License 2.0.
More from this week
- Stroq Check AI coding agent sessions for leaked keys
Stroq scans your recent Claude Code and Codex sessions for keys that left your machine.
- agent-desktop Let AI agents read and click desktop apps
For developers building computer-use agents: agent-desktop lets an AI agent read and operate desktop apps on Mac, Windows or Linux from a command line.
- Auto-Ontology Give AI agents checked business meanings for your database
Help AI agents answer questions about company databases using reviewed definitions and SQL, with each answer showing its steps.
Explore by topic
Post this
 Download share image
For makers
Made this? Show it’s on BuildTube — add the badge to your README or embed the card on your site.
README badge (Markdown)
[](https://buildtube.app/p/gh-usestrix-strix/)Embed card (HTML)
<iframe src="https://buildtube.app/embed/gh-usestrix-strix/" width="560" height="240" style="border:0;max-width:100%" loading="lazy" title="Strix on BuildTube"></iframe>